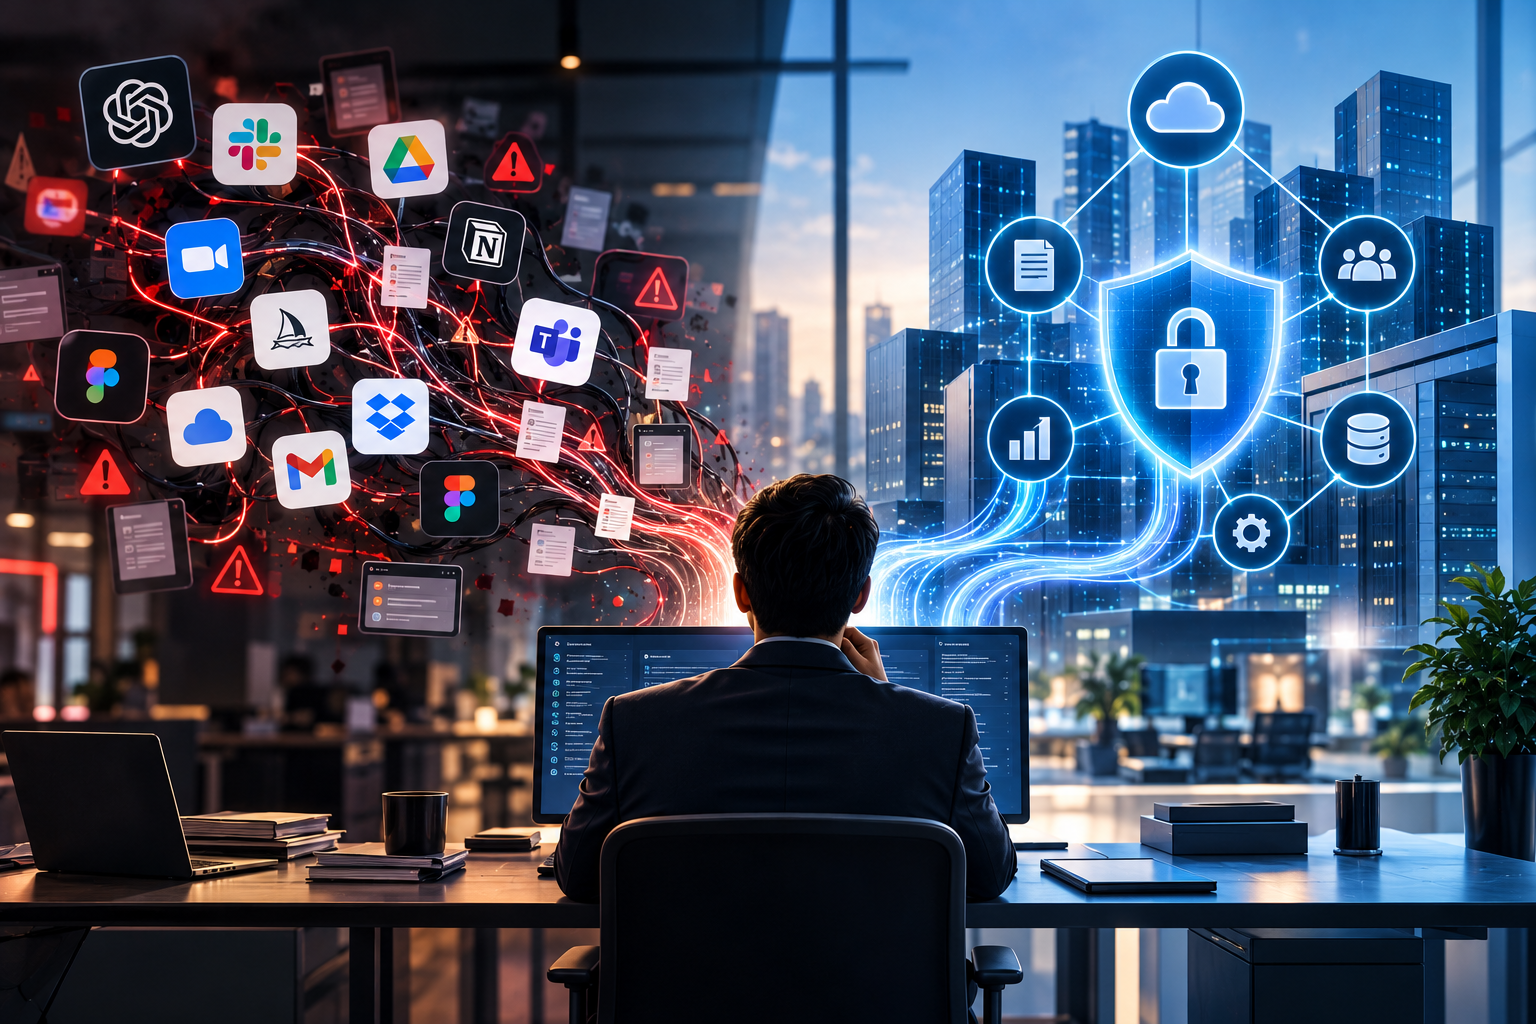
Technology adoption rarely waits for formal approval. An employee signs up for a productivity tool to simplify a task. A department adopts a new cloud platform to manage its data. A developer experiments with an AI assistant to speed up coding. Each decision may appear harmless on its own, but together, they can create a layer of technology operating beyond the visibility and control of the organisation.
This is the growing challenge of shadow IT and shadow AI.
As enterprises adopt cloud services, SaaS applications, automation tools, and generative AI, the boundary between approved and unapproved technology is becoming increasingly difficult to manage. Employees are finding faster ways to work, but organisations may be losing sight of where their data resides, how it is processed, and who has access to it.
The answer is not simply to restrict new technology. It is to build an IT environment where innovation can happen without compromising security, compliance, or operational resilience.
What Are Shadow IT and Shadow AI?
Shadow IT refers to hardware, software, cloud services, applications, and digital systems used within an organisation without the knowledge, approval, or oversight of its IT team.
It can take many forms, from an employee storing company documents in a personal cloud account to a department purchasing a SaaS subscription without a security review. Even well-intentioned decisions can introduce vulnerabilities when they bypass established IT processes.
Shadow AI is an extension of this challenge. It involves using artificial intelligence tools, models, plugins, or AI-powered workflows without appropriate organisational approval or governance.
For example, employees might upload internal documents to public AI platforms to generate summaries, use unapproved AI tools to analyse customer information, or connect an AI assistant to company systems without assessing the permissions it requires.
The distinction matters because AI introduces risks that traditional software governance may not fully address. An AI application may process sensitive information, generate inaccurate recommendations, retain interaction data under certain conditions, or take actions through connected tools.
According to Microsoft’s guidance on shadow AI, unmanaged AI applications can create data leakage, compliance, security, and auditability challenges. The issue is not necessarily that employees are using new technology. It is that the organisation may not have the visibility and controls needed to manage that usage responsibly.
Why Shadow Technology Is Becoming More Common
Shadow IT is not a new enterprise problem, but the pace and accessibility of modern technology have changed its scale.
Cloud platforms make it possible to deploy applications without purchasing physical infrastructure. SaaS products allow business teams to subscribe directly to tools. AI assistants can generate reports, analyse information, write code, and automate repetitive tasks with minimal technical expertise.
This convenience creates a gap between how quickly employees can adopt technology and how quickly an organisation can evaluate it.
The pressure to work faster
Employees are often measured on outcomes, not on how long it takes to navigate internal approval processes. When an approved tool feels inadequate or difficult to access, people may look for alternatives.
A marketing team might adopt an AI writing tool. A finance team might experiment with an external data-analysis platform. A developer might use an AI coding assistant to accelerate delivery.
These decisions are often driven by productivity rather than an intention to bypass security. However, when teams make them independently, IT loses the opportunity to assess the technology before it becomes part of everyday operations.
Decentralised technology purchasing
Business units increasingly have access to their own budgets and can purchase digital services directly. This flexibility can help organisations move faster, but it can also create fragmented technology environments.
Multiple teams may pay for overlapping tools, use different platforms to store similar information, or establish integrations without considering the wider enterprise architecture.
Over time, this creates unnecessary costs, inconsistent processes, and a growing inventory of systems that are difficult to manage centrally.
The rapid expansion of AI capabilities
AI has lowered the barrier to experimentation even further. Employees no longer need extensive technical knowledge to automate a task or build a basic workflow.
AI functionality is also appearing inside existing applications, browsers, development environments, and collaboration platforms. As a result, shadow AI is not limited to standalone chatbots. It can exist within connected workflows, third-party integrations, and AI agents capable of interacting with business systems.
This makes visibility increasingly important. Organisations need to understand not only which applications employees use, but also how AI capabilities access and process enterprise data.
The Hidden Risks of Unmanaged Enterprise Technology
The impact of shadow IT and shadow AI extends beyond an unauthorised software subscription. When unmanaged tools become embedded in business operations, they can create security, financial, regulatory, and architectural challenges.
1. Sensitive data exposure
One of the most significant risks is the movement of business information into environments that have not been reviewed or approved.
Employees may upload contracts, financial reports, customer records, source code, internal presentations, or proprietary documents to external platforms. Depending on the service and its configuration, that information may be processed, retained, or made accessible in ways the organisation has not evaluated.
AI adds another layer of complexity because employees may share information through prompts, uploaded files, connected applications, or automated workflows without fully understanding how the data is handled.
Organisations therefore need clear rules about data classification, approved tools, retention, and the types of information employees can share with external services.
2. Security vulnerabilities and unauthorised access
Every new application or integration can expand an organisation’s attack surface.
An unapproved service may lack appropriate authentication controls, security monitoring, encryption requirements, or regular vulnerability assessments. Employees may also grant applications permissions that exceed what they need to perform their tasks.
In AI-enabled environments, an assistant connected to email, documents, databases, or business applications may inherit access to sensitive information. If those permissions are excessive or poorly monitored, a compromised account or unsafe workflow can have consequences beyond a single application.
Effective security requires visibility into connected services, consistent identity management, least-privilege access, and continuous monitoring.
3. Compliance and audit challenges
Enterprises must understand where regulated or sensitive data is stored, how it is processed, and which parties can access it. Unapproved technology can make these responsibilities harder to fulfil.
If employees use external platforms to process customer information, confidential records, or regulated data, the organisation may struggle to demonstrate that appropriate safeguards and contractual requirements are in place.
AI can introduce additional questions about how outputs were generated, which information influenced a decision, and whether relevant records have been retained.
A technology inventory, documented approval process, and appropriate audit trails help organisations establish accountability without preventing legitimate experimentation.
4. Rising costs and technology duplication
Shadow IT also creates a financial problem.
Different departments may purchase tools that perform similar functions, maintain subscriptions that are no longer needed, or create workflows that duplicate existing enterprise capabilities. Costs can increase further when teams deploy cloud resources or AI services without clear ownership and usage monitoring.
These expenses are not always visible in central IT budgets. They may appear as departmental subscriptions, individual reimbursements, or consumption-based charges that grow gradually.
A consolidated view of software subscriptions, cloud usage, licences, and AI consumption can help enterprises identify duplication and improve technology spending decisions.
5. Fragmented architecture and operational complexity
A well-designed enterprise architecture connects applications, data, infrastructure, and business processes through clear standards and interfaces.
Unmanaged technology can weaken that structure. Teams may create isolated data stores, establish unsupported integrations, or introduce applications that cannot exchange information reliably with existing systems.
As these solutions become business-critical, replacing or integrating them becomes increasingly difficult.
The result is a more complicated technology landscape, with inconsistent data, duplicated processes, and dependencies that may be poorly documented.
6. Unreliable AI outputs and decisions
Shadow AI introduces a risk that extends beyond traditional information security.
Employees may rely on AI-generated analysis, code, recommendations, or customer communications without checking accuracy, context, or suitability. When AI outputs influence business decisions, errors can affect customer experiences, operational processes, and organisational reputation.
The risk increases when AI systems operate with little human oversight or are connected to tools that allow them to take actions.
Organisations should establish clear expectations for human review, approved use cases, testing, and accountability, particularly where AI outputs influence consequential decisions.
Why a Blanket Ban Is Rarely the Right Solution
When organisations discover shadow technology, the immediate response may be to block applications or prohibit unauthorised AI use. Restrictions can be appropriate for tools that present unacceptable risks, but a blanket ban does not necessarily resolve the underlying problem.
Employees still need to complete their work. If approved alternatives are unavailable, inconvenient, or ineffective, they may continue using unapproved services through personal accounts or less visible channels.
The organisation then loses even more visibility.
A better approach is to understand why employees are adopting these tools and provide secure, practical alternatives. This means combining technology controls with clear policies, accessible support, and an approval process that reflects the pace of business.
The objective should be to make responsible technology adoption easier than working around IT.
How Enterprises Can Manage Shadow IT and Shadow AI
Managing unmanaged technology requires a coordinated approach across IT, cybersecurity, enterprise architecture, compliance, procurement, and business leadership.
Establish visibility across the technology environment
The first step is to understand what is already being used.
Organisations can review software inventories, cloud activity, identity and access logs, network traffic, procurement records, and available endpoint security signals to identify applications and services that may be operating outside approved processes.
AI discovery should be part of this effort. Enterprises need to identify relevant AI applications, browser-based services, model endpoints, integrations, and automated workflows where technically possible.
The resulting inventory should record ownership, purpose, data access, business criticality, and risk. Discovery should be ongoing rather than a one-time exercise, because technology usage changes continuously.
Create a clear technology approval framework
Not every tool requires the same level of scrutiny. A low-risk productivity application does not present the same concerns as a platform that processes confidential customer data or connects to critical business systems.
A risk-based approval framework helps organisations distinguish between acceptable experimentation, use that requires additional safeguards, and applications that should be restricted.
Security, privacy, legal, procurement, and architecture teams should have clearly defined responsibilities. Approval requirements should be proportionate to the data involved, the permissions requested, and the potential business impact.
This makes governance more practical while ensuring that higher-risk deployments receive appropriate attention.
Define an enterprise AI governance policy
AI governance should address how employees can use AI tools, what information they may share, and which activities require human review.
A useful policy should cover approved tools, data handling, access permissions, output validation, third-party integrations, record retention, and accountability for AI-assisted decisions.
It should also address AI agents and automated workflows. These systems may interact with multiple applications or perform actions on behalf of users, making permissions, logging, testing, and escalation procedures particularly important.
Policies must be supported by practical guidance and regular communication. Employees are more likely to follow the rules when they understand the risks and know which approved alternatives are available.
Strengthen identity, access, and data controls
Technology governance becomes more effective when supported by consistent security controls.
Enterprises should apply single sign-on where supported, multifactor authentication, least-privilege access, and regular access reviews. Data loss prevention and data classification controls can help reduce the risk of sensitive information leaving approved environments.
Where appropriate, organisations should also use application controls, API governance, endpoint monitoring, and centralised logging to improve visibility across their technology landscape.
For AI systems, access should be limited to the data and actions necessary for the intended use case. Connections to business applications should be reviewed carefully, and high-impact actions should have suitable approval or human oversight.
Align technology adoption with enterprise architecture
An effective enterprise architecture strategy provides a framework for evaluating how new tools fit into the wider IT environment.
Before adopting a new application, organisations should consider whether an existing platform already provides the required capability, how the tool will integrate with current systems, and whether it introduces new data or operational dependencies.
This approach reduces duplication and supports long-term scalability. It also helps ensure that individual teams can innovate without creating disconnected technology environments that become difficult to maintain.
Monitor usage, cost, and risk continuously
Approval alone is not enough. Organisations need to understand how technology is being used after deployment.
Regular reviews can identify inactive subscriptions, unexpected cloud consumption, excessive permissions, unapproved integrations, and changes in how applications process data.
AI services may also require monitoring for usage patterns, output quality, access anomalies, and changes in the scope of automated actions.
Clear ownership and measurable indicators help leaders assess whether governance is working. Useful measures include the number of identified and assessed applications, the percentage of high-risk tools with assigned owners, policy exceptions, remediation timelines, and technology spending that can be attributed to specific business functions.
Turning Technology Governance into a Business Advantage
Shadow IT and shadow AI are often treated purely as security problems. In reality, they can reveal something important about how an organisation works.
When employees repeatedly adopt the same unauthorised tools, it may indicate gaps in existing systems, slow procurement processes, limited access to approved AI capabilities, or unmet business needs.
These patterns can help technology leaders identify opportunities to improve internal platforms, simplify workflows, and make approved solutions more accessible.
The goal is not to eliminate experimentation. It is to create an environment in which experimentation can be evaluated, supported, and scaled responsibly.
For enterprises pursuing cloud modernisation, AI adoption, or infrastructure transformation, this requires more than a policy document. It requires an integrated approach to architecture, security, data governance, managed services, and operational oversight.
The Role of Enterprise IT Partners
Managing shadow technology can be challenging for organisations with complex application portfolios, hybrid infrastructure, multiple cloud environments, and distributed teams.
An experienced enterprise IT partner can help assess the existing technology landscape, identify governance gaps, strengthen infrastructure controls, and establish practical processes for managing new technology adoption.
This work can include enterprise architecture assessments, cloud and infrastructure reviews, application rationalisation, security and access improvements, and the development of governance frameworks aligned with business priorities.
For organisations exploring AI, the focus should be on enabling secure adoption rather than treating every new tool as a threat. The right combination of architecture, controls, and ongoing management can help businesses capture the benefits of innovation while reducing avoidable risks.
Conclusion
Shadow IT and shadow AI are symptoms of a technology environment that is evolving faster than traditional governance processes can keep up with.
Employees will continue to seek tools that help them work more efficiently, and AI will make experimentation even more accessible. Organisations that respond only with restrictions may push this activity further out of sight. Those that combine visibility, risk-based governance, secure alternatives, and continuous monitoring can manage it more effectively.
Ultimately, the challenge is not simply to control which technologies employees use. It is to ensure that every tool, application, and AI-enabled workflow contributes to business outcomes without creating unnecessary exposure.
When enterprise governance supports innovation rather than obstructing it, technology becomes easier to manage, safer to scale, and better aligned with the organisation’s long-term goals.